Indian registry checks
Company register (MCA), PAN, GST returns, litigation and PEP through Surepass, for Indian vendors of UAE firms.
The platform
Each section has a demo that runs in your browser with fictional data. Panels for features still in build are labelled Preview.
NexaVerify · onboarding checks Live
Trade licence, TRN, IBAN, beneficial owner and sanctions screening for UAE vendors, alongside the registry and bank checks NexaPair already runs for Indian vendors. Each row says whether that check is live in the product or runs on this site as a format check.
These run in your browser and send nothing anywhere. They test structure only, not whether the number is registered or who holds it.
Company register (MCA), PAN, GST returns, litigation and PEP through Surepass, for Indian vendors of UAE firms.
A test deposit through Meon confirms who owns the account. Aadhaar eSign for documents.
Consolidated sanctions and politically exposed person lists through OpenSanctions, re-checked while the vendor is active.
Licence status and expiry, mainland or free zone.
Tax registration confirmed for VAT and corporate tax.
Who ultimately owns or controls the vendor, compared with what the vendor declared.
Screening of the company, owners and directors against the lists UAE firms must apply.
Used by: Procurement at intake, Finance before payment, Compliance for due diligence.
NexaGraph · relationship intelligence Live
Shared directors, bank accounts, phone numbers and addresses across your vendors and employees, found while you type and before the vendor is saved.
Phones, addresses, bank accounts and similar names matched against your employee list.
Shared directors, tax numbers and bank accounts across your vendor base.
Every link comes with its evidence. Confirmed related parties go to the Board.
Where many vendors rely on the same providers behind the scenes.
Used by: Procurement and HR to keep conflicts out, Compliance and the Board to approve related parties.
NexaScore · explainable risk Live
Every factor is shown with its weight, beside minimum-tier rules you can audit. The tier decides the due diligence, the review cycle and the approvals.
Every factor and weight visible, and set by your own risk model.
Floors for sensitive data, sanctions findings and staff links that no total can override.
The tier opens the right case, with the right checks and review cycle.
Vendors mapped to critical operations, with recovery time checked against your tolerance.
Used by: Risk to own the model, Information Security and Operations to set access and resilience, Audit to test it.
NexaSentinel · always-on monitoring Live
Sanctions lists, filings, court records and financial health are checked every day, and each change becomes an alert for the vendor's owner. When a vendor incident touches a critical operation, the reporting clocks for your regulator start.
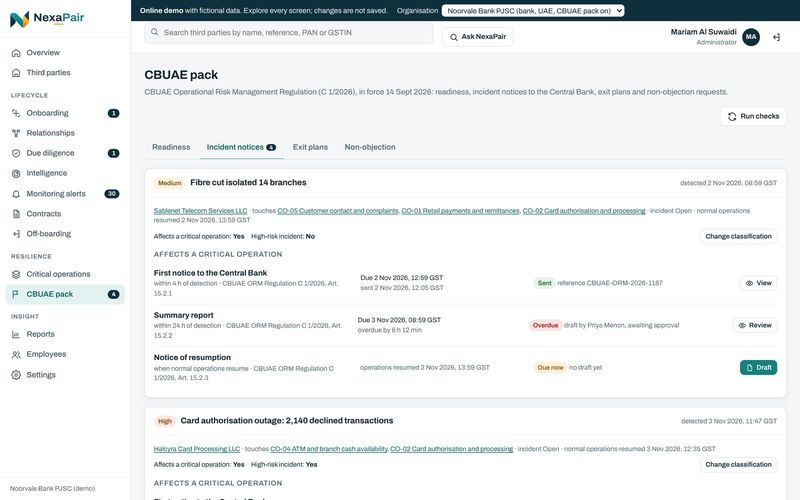
Sanctions, GST filing, litigation and financial-health changes, checked across every active vendor.
Each alert goes to the person who owns the vendor. It is taken, worked and closed with a note for the audit trail.
Each vendor incident is logged with its impact, actions and lessons learned, linked to the vendor.
Clocks that start when an incident touches a critical operation, with drafts ready for approval. Live for each UAE regime you select, from the CBUAE's 4-hour notice to the rules that say "immediately".
Used by: Compliance for sanctions, Finance for tax and credit, Legal for court cases, and Operations for incidents.
NexaPilot · AI under your control Live
Today NexaPilot reads and drafts for your analysts. Next, it decides in the background while its accuracy is measured. It acts on its own only in categories where it has proved itself, and only if you allow it.
Built-in analysis, Claude, OpenAI, Azure OpenAI, or a private model in your own environment.
Emails, phone numbers and bank accounts are removed before sending. Keys are encrypted with AES-256-GCM.
Switched on feature by feature. Every output is labelled as AI, and a person makes the decision.
Accuracy measured per category, autonomy only where you allow it, and an automatic step back if it drifts.
Used by: Risk and Compliance heads to set the bar, Internal Audit to test it, and the Board risk committee to approve it.
Resilience · critical operations, exits and change Live
Map each critical operation to the vendors and subcontractors behind it, compare their recovery time with your tolerance, keep an exit plan for each, and stop a material change from going live before your regulator has been told.
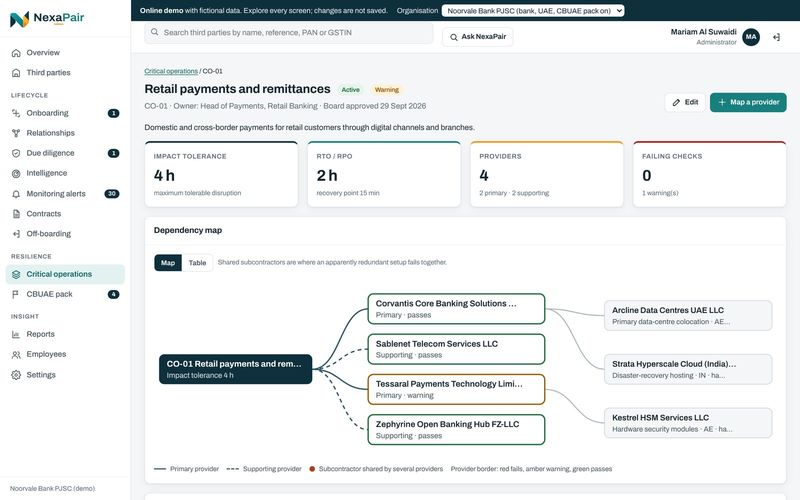
Each critical operation with its owner, tolerance and the vendors behind it.
The subcontractors behind each vendor, and where they overlap.
Recovery times against tolerance, and single points of failure across operations.
A plan for each critical arrangement, with alternatives and a test date.
A go-live gate that stays closed until the regulator's response is on file.
A check that the master record stays where your regulator expects it.
Used by: Operations and business owners to map services, Risk to set tolerances, Legal and Compliance to handle notices.
Assess · questionnaires and evidence review Live
Send vendors a questionnaire in the language they prefer. When the answers and evidence come back, the AI checks whether the evidence supports each answer, and a person decides.
Questionnaires in Arabic and English, sized to the vendor's tier.
Each answer compared with the document behind it, with the reason shown.
AI output is labelled, personal data is removed first, and an analyst signs off.
The whole product in Arabic, for your teams and your vendors.
Used by: Information Security and Compliance to assess vendors, vendors themselves through the supplier portal.
Cyber posture · outside-in signals Live
Passive checks of what any visitor can see: email security records, the certificate and TLS versions, security headers and security.txt. No port scanning, no probing, and nothing for the vendor to install.
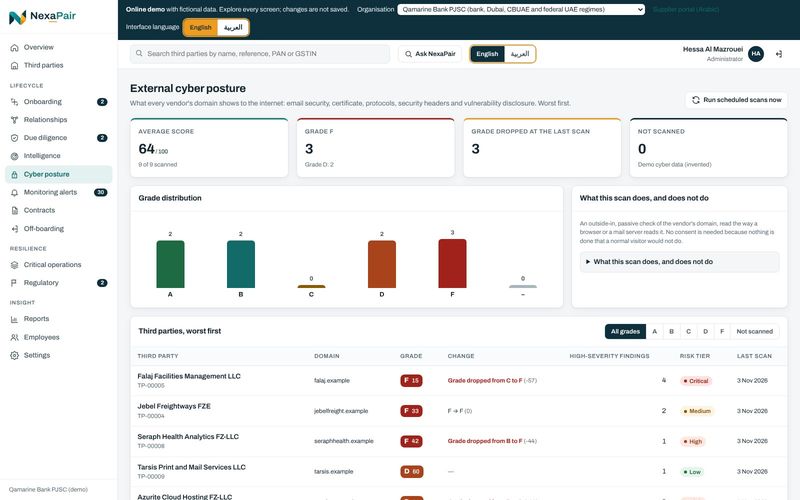
MX, SPF and DMARC, which make it harder to impersonate a vendor by email.
Certificate trust and expiry, old TLS versions, the redirect to HTTPS, six security headers and security.txt.
An A to F grade, re-checked on a schedule set by tier. A drop raises an alert, and the grade can count in NexaScore if you choose.
Used by: Information Security to watch vendors from the outside, Procurement to see posture at intake.
Integrations Live
Vendor requests come in from your ERP and procurement tools. Risk tiers, payment holds and alerts go back out. Connect today with the REST API, signed webhooks and exports. Native connectors are on the roadmap.
Create and update third parties, sync employees for conflict checks, and read scores and cases. Keys are scoped by role, with OpenAPI documentation at /api/docs.
13 events, each signed with an HMAC-SHA256 signature and logged with its delivery result. Teams and Slack formats are built in.
Ten registers, including the outsourcing register, alerts, findings, contracts and the audit trail.
For your developers
Check the signature (Node.js)
const crypto = require('crypto');

function verify(header, rawBody, secret) {
  const parts = Object.fromEntries(
    header.split(',').map((p) => p.split('='))
  );
  const expected = crypto
    .createHmac('sha256', secret)
    .update(parts.t + '.' + rawBody)
    .digest('hex');
  return parts.v1.length === expected.length &&
    crypto.timingSafeEqual(
      Buffer.from(parts.v1), Buffer.from(expected));
}
Every delivery is logged in NexaPair with its response code, so you can see what arrived and send a test from Settings.
Every result is stored with where it came from and when.
India's company register (MCA), PAN, GST returns, court cases and PEP checks.
Bank-account checks for Indian accounts: a small test deposit confirms the owner. Plus Aadhaar eSign.
Consolidated sanctions and politically exposed person lists, re-checked while the vendor is active.
Already pay for a screening or ratings service? A provider template connects any HTTP API to the same checks.
Trade licence, TRN and beneficial-owner checks for UAE vendors.