UAE edition · one platform for six regulatory regimes
Third-party risk, built around UAE regulation.
NexaPair verifies vendors, finds hidden links between suppliers and your own staff, and maps every step to what your regulator expects. Every feature on this site is marked Live, Preview or Coming soon.
Find your regulator- Honest status on every feature
- Deployable in a UAE cloud region
- English and Arabic
- Fictional data in every demo
- Trade licenceDubai free zone · activeLive
- TRN15 digits · format validFormat check
- IBANStructure and checksum validFormat check
- Beneficial owners2 declared · register check pendingLive
- UAE and UN listsNo matchLive
- Staff linkA director's mobile matches an employeeLive
Fictional vendor · demo data
Your regulator
Pick a regime to see what it expects of vendor risk.
A short orientation for each regime, and how NexaPair covers it today. Each regulator page carries the full requirement map.
Central Bank of the UAE
Applies to: Banks, finance companies, insurers, exchange houses and payment service providers licensed onshore.
What it expects
- Obtain a CBUAE notice of non-objection before outsourcing any activity whose disruption could significantly affect Critical Operations. CBUAE Operational Risk Management Regulation Art. 13.5
- No third-party arrangement without first doing a risk assessment and due diligence. CBUAE Operational Risk Management Regulation Art. 13.3
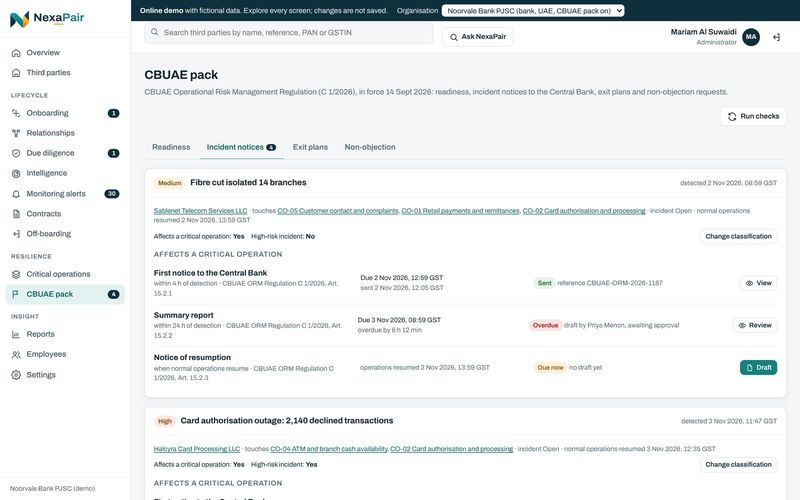
- For operational risk events that significantly affect, or may affect, Critical Operations (e.g. events that trigger BCP or DR, or materially affect customers, operations, profit or capital): first notify the CBUAE, naming the affected Critical Operations. CBUAE Operational Risk Management Regulation Art. 15.2, 15.2.1
- The Master System of Record, including all Confidential Data, must be continuously maintained and stored in the UAE. Foreign bank branches may keep a UAE copy updated at least daily, with CBUAE approval. CBUAE Outsourcing Regulation for Banks Art. 6.1, 6.2
- Contracts must oblige the provider to comply with CBUAE requests and reporting, and to allow CBUAE on-site examinations for Critical Operations outsourcing. CBUAE Operational Risk Management Regulation Art. 13.7
How NexaPair covers it
- LiveBoard pack
- LiveReadiness view for each regulator, also in the Board pack
- LiveEquivalent-resilience and concentration checks
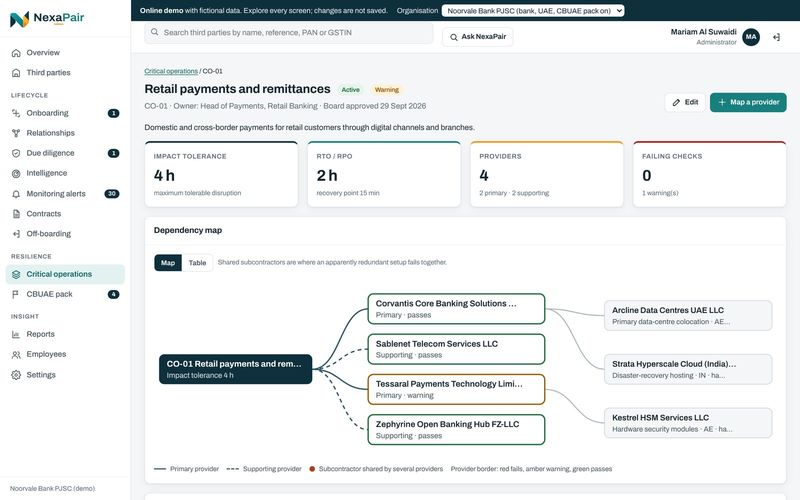
- LiveVendor and subcontractor (fourth-party) mapping
- LiveCritical-operations register
- LiveDue diligence cases by tier
- LiveExplainable risk score with factor weights and minimum-tier rules
- LiveMaterial-change notice and non-objection gate
Summarised from our source-by-source regulatory map. Items marked To be confirmed are still being checked. Not legal advice.
Open the CBUAE pageDubai Financial Services Authority (DIFC)
Applies to: Firms authorised by the DFSA in the Dubai International Financial Centre.
What it expects
- Inform the DFSA of any material outsourcing arrangement. DFSA GEN outsourcing rules GEN 5.3.22(1)
- Do due diligence when choosing providers, supervise the outsourced work effectively, and deal with any provider act or failure that could breach DIFC law. DFSA GEN outsourcing rules GEN 5.3.21(3)
- The controller notifies the Commissioner of a personal data breach. DIFC Data Protection Law Art. 41(1)
- The written contract must require the provider to supply information, give access to its premises, and deal openly and cooperatively with the DFSA. DFSA GEN outsourcing rules GEN 5.3.22(2)(b), (3)
- Sub-processors need the controller's prior written authorisation. A general authorisation is allowed if the processor gives notice of changes and considers objections. DIFC Data Protection Law Art. 24(2)
How NexaPair covers it
- LiveBoard pack
- LiveReadiness view for each regulator, also in the Board pack
- LiveDue diligence cases by tier
- LiveExplainable risk score with factor weights and minimum-tier rules
- LiveMaterial-change notice and non-objection gate
- LiveOutsourcing register
- LiveCritical-operations register
- LiveEquivalent-resilience and concentration checks
Summarised from our source-by-source regulatory map. Items marked To be confirmed are still being checked. Not legal advice.
Open the DFSA pageFinancial Services Regulatory Authority (ADGM)
Applies to: Firms authorised by the FSRA in Abu Dhabi Global Market.
What it expects
- Inform the Regulator about material outsourcing arrangements. Secondary source FSRA GEN outsourcing rules GEN 3.3.32(1)
- Identify outsourcing of functions directly related to Regulated Activities. Do due diligence on suitability, supervise effectively, and act on provider failures. FSRA GEN outsourcing rules GEN 3.3.31(1), 3.3.31(3)(a)-(c)
- Notify the FSRA of a suspected material cyber incident immediately on discovery, with a 24-hour backstop for the initial report (Template A) emailed to incidents.fsra@adgm.com, copying the supervisor. Progress updates (Template B) follow at a frequency the supervisor sets. FSRA Cyber Risk Management Rules GEN 3.5.18; GEN 8.10
- Keep a cyber incident response plan and test it. The UAE Cyber Security Council's national plan can serve as a reference. FSRA Cyber Risk Management Rules GEN 3.5.16
- Material outsourcing needs a written contract covering the prescribed factors. The FSRA expects performance metrics and default and termination clauses, and that contracts are not signed before due diligence. FSRA GEN outsourcing rules GEN 3.3.32(3)
How NexaPair covers it
- LiveDue diligence cases by tier
- LiveExplainable risk score with factor weights and minimum-tier rules
- LiveMaterial-change notice and non-objection gate
- LiveOutsourcing register
- LiveContracts and obligations
- LiveCSV and JSON exports of 10 registers, including the audit trail
- LiveAlerts for sanctions, GST filing, financial health and litigation
- LiveSanctions and PEP screening via OpenSanctions
Summarised from our source-by-source regulatory map. Items marked To be confirmed are still being checked. Not legal advice.
Open the FSRA pageCapital Market Authority (formerly the Securities and Commodities Authority)
Applies to: Onshore capital-market firms formerly licensed by the SCA, which became the CMA on 1 January 2026. Virtual assets now sit within the CMA's federal remit too.
What it expects
- The 2024 amendments added outsourcing requirements for licensed firms. The location in the Rulebook, the conditions, and any approval or notification duty to the regulator were NOT verified. To be confirmed SCA (now CMA) Rulebook for Financial Activities
How NexaPair covers it
- LiveMaterial-change notice and non-objection gate
- LiveOutsourcing register
Summarised from our source-by-source regulatory map. Items marked To be confirmed are still being checked. Not legal advice.
Open the CMA (formerly SCA) pageVirtual Assets Regulatory Authority (Dubai)
Applies to: Virtual asset service providers licensed in Dubai, including its free zones other than the DIFC.
What it expects
- Notify VARA before any cross-border outsourcing, and promptly if an overseas authority seeks access to VASP information. VARA Company Rulebook - Part IV Outsourcing Part IV, Section F
- Risk-assess each arrangement, including materiality. Due diligence covers capacity, financial soundness, reputation, regulatory status, reliance on subcontractors and virtual-asset expertise. VARA Company Rulebook - Part IV Outsourcing Part IV, Section B
- Notify VARA of a material breach of a Material Outsourcing agreement, or a development that could significantly affect operations, finances or reputation. VARA Company Rulebook - Part IV Outsourcing Part IV, Section H.1-H.2
- For material outsourcing, the VASP, VARA and appointed bodies get full access to premises, systems, data and staff. Pooled audits and certifications cannot replace the VASP's own audit right. VARA Company Rulebook - Part IV Outsourcing Part IV, Section G
- Sub-outsourcing terms are required. The provider notifies planned changes, and the VASP may object or terminate. VARA Company Rulebook - Part IV Outsourcing Part IV, Section E
How NexaPair covers it
- LiveBoard pack
- LiveReadiness view for each regulator, also in the Board pack
- LiveDue diligence cases by tier
- LiveExplainable risk score with factor weights and minimum-tier rules
- LiveOutsourcing register
- LiveCSV and JSON exports of 10 registers, including the audit trail
- LiveContracts and obligations
- LiveVendor and subcontractor (fourth-party) mapping
Summarised from our source-by-source regulatory map. Items marked To be confirmed are still being checked. Not legal advice.
Open the VARA pageGovernment entities and critical sectors
Applies to: Federal and local government entities, and operators of critical infrastructure such as energy, telecoms, health and transport.
What it expects
- Background verification of contractors and third-party users before access, and revocation of access within 24 hours of exit. ADHICS v2 HR 2.1; HR 4.3
- Entities must report threats, hacks, leaks, interceptions or risks to DESC. Dubai Electronic Security Centre Law Art. 14(4)
- Health information (PII, PHI or copies) must not be stored, processed or transferred outside the UAE without a valid, specific DoH exemption. ADHICS v2 CO 9.2 (item 6)
- Third-party assessors must not keep assessment data after the engagement; it must be erased from their assets. ADHICS v2 CO 7.2
- Third parties must notify the entity in advance of changes, including relocation, reconfiguration and onboarding of sub-contractors. ADHICS v2 CO 2.3 (item 5)
How NexaPair covers it
- LivePassive outside-in cyber posture: an A to F grade per vendor, history, scheduled re-checks and grade-drop alerts
- LiveQuestionnaires in Arabic and English with AI evidence review that a person signs off
- LiveDue diligence cases by tier
- LiveExplainable risk score with factor weights and minimum-tier rules
- LiveCritical-operations register
- LiveEquivalent-resilience and concentration checks
- LiveIncident records
- LiveIncident reporting clocks across regulators: CBUAE, ADGM and the "immediately" rules
Summarised from our source-by-source regulatory map. Items marked To be confirmed are still being checked. Not legal advice.
Open the Government and critical sectors pageFederal law applies alongside every regime: data protection, AML and sanctions, beneficial ownership, tax registration, anti-bribery and cybercrime. See federal law
Notification clocks
Six regulators, very different clocks.
Write the shortest clock that applies to you into vendor contracts, so the vendor tells you well inside it. For a CBUAE institution that is 4 hours; for an ADGM firm it is 24 hours, running through weekends.
- 4 hCBUAE · an event significantly affecting a critical operationCBUAE Operational Risk Management Regulation Art. 15.2, 15.2.1
- 72 hCBUAE · a high-risk incident under the Board's criteria, a separate triggerCBUAE Operational Risk Management Regulation Art. 15.3
- Now · 24 h maxFSRA (ADGM) · a suspected material cyber incident, weekends includedFSRA Cyber Risk Management Rules GEN 3.5.18; GEN 8.10
- ImmediatelyDESC (Dubai) · threats, hacks, leaks or interceptionDubai Electronic Security Centre Law Art. 14(4)
- ImmediatelyVARA · a material breach of a Material Outsourcing agreementVARA Company Rulebook - Part IV Outsourcing Part IV, Section H.1-H.2
- 24 hSanctions · freeze funds after a listing decisionTargeted Financial Sanctions regulation Art. 15 (freezing)
Start here
New to third-party risk in the UAE? Start with these.
For every team
One dial. Every department. Three steps each.
Nobody needs to be a vendor-risk expert. Turn the dial to your team and NexaPair shows what to do, while it runs the checks behind the scenes.
Procurement
Bring a new vendor in.
Your three steps
- 1Type the vendor's name and trade licence number
- 2Pick the service they will provide
- 3Send the secure supplier link
NexaPair does the rest
- Duplicates and links to your staff flagged as you type
- Trade licence, TRN and beneficial owner checked
- Risk tier set, with the checks that tier needs
What you see: a clear next step: proceed, or exactly what is missing.
Walk through onboardingFinance and Accounts Payable
Pay the right party, every time.
Your three steps
- 1Open the vendor
- 2Look at the bank badge
- 3Release or hold the payment
NexaPair does the rest
- Account owner confirmed by test deposit for Indian accounts
- Accounts shared with employees or other vendors flagged
- UAE IBAN and TRN checks at entry
What you see: green means pay; anything else comes with the reason.
Check an IBANLegal
Sign contracts that hold up.
Your three steps
- 1Attach the agreement
- 2Read the clause checklist
- 3Approve, or send it back with notes
NexaPair does the rest
- Audit rights, regulator access, data location and termination checked
- Service levels and obligations tracked after signing
- Missing subcontractor terms flagged
What you see: every gap named before signature.
See what your regulator expectsCompliance
Screen once, decide with confidence.
Your three steps
- 1Open the due diligence case
- 2Read the AI risk brief
- 3Clear, mitigate or escalate each finding
NexaPair does the rest
- Sanctions and PEP screening through OpenSanctions
- UAE Local Terrorist List and UN list screening
- AI triage gives a second opinion on every hit
What you see: a decision with its evidence attached.
Run the checksInformation Security
Grant access only where it is safe.
Your three steps
- 1Answer three questions on data and systems
- 2Review the security findings
- 3Set the access level
NexaPair does the rest
- Data and system access raise the minimum tier
- Questionnaire in Arabic and English with AI evidence review
- Outside-in checks of email security, certificates and headers
What you see: access matched to risk, with the reasons recorded.
Try the questionnaireOperations and business owners
Know who keeps your services running.
Your three steps
- 1Pick the critical operation
- 2Confirm the vendor's recovery time
- 3Check the exit plan
NexaPair does the rest
- Vendors and their subcontractors mapped to critical operations
- Recovery time compared with your tolerance
- CBUAE incident notices tracked against their clocks; other regulators to follow
What you see: resilience gaps visible before an outage.
Map a critical operationHuman Resources
Keep conflicts of interest out.
Your three steps
- 1Keep the employee list in sync
- 2Review the people NexaPair flags
- 3Confirm or dismiss each link
NexaPair does the rest
- Staff phones, addresses and bank accounts matched against vendors
- Name similarity scored, so near-matches surface too
- Confirmed related parties routed to the Board
What you see: conflicts found before the first invoice.
Find a hidden linkRisk Management
Own the model, not the paperwork.
Your three steps
- 1Set tiers, weights and thresholds
- 2Review the portfolio dashboard
- 3Approve exceptions
NexaPair does the rest
- Every score explained, factor by factor
- Concentration across shared providers
- Board pack generated on demand
What you see: a portfolio view the Board can trust.
Build a scoreInternal Audit
Test the evidence, not memories.
Your three steps
- 1Open the audit trail
- 2Sample any decision
- 3Export the evidence
NexaPair does the rest
- Decisions and changes logged with who and when
- AI outputs labelled and kept in a usage log
- Registers export to CSV or JSON in one click
What you see: evidence ready before the auditor asks.
See how the AI is governedBoard and executive management
Oversee vendor risk without chasing it.
Your three steps
- 1Open the Board pack
- 2Review the top risks
- 3Approve related parties
NexaPair does the rest
- Material and critical vendors summarised
- Related-party approvals queued for decision
- Readiness against each regulator, requirement by requirement
What you see: accountability the regulator can see.
See the Board packThe platform
Eight engines, each with a demo you can try.
New in the product Live
Now live for CBUAE-licensed institutions.
Critical operations mapped to the vendors behind them, and CBUAE incident notices tracked against their clocks. Other regulators follow.
UAE checks
The checks a UAE vendor file needs.
In the product, the licence, TRN and owners are recorded with the evidence a reviewer checks, and every owner is screened. On this site, some run as format checks. Each one says which.
- Trade licenceLiveStatus and expiry, mainland or free zone.
- Tax registration (TRN)LiveRegistration for VAT and corporate tax. Format check runs on this site.
- IBAN structure and checksumFormat checkA genuine check you can run here, before any payment detail is saved.
- Beneficial ownerLiveWho ultimately owns or controls the vendor.
- UAE Local Terrorist List and UN listLiveScreening against the lists UAE firms must apply.
- Sanctions and PEPLiveConsolidated lists through OpenSanctions, re-checked while the vendor is active.
- Indian vendors, checked at the sourceLiveCompany register, PAN, GST, litigation and bank-account owner, for cross-border suppliers.
- PDPL cross-border transfersLiveA check before personal data goes to a vendor outside the UAE.
Interactive walkthrough · about 4 minutes
Onboard a critical UAE vendor yourself, start to finish.
A UAE bank brings on a Dubai cloud payments provider. You play six departments in turn and click the glowing button at each step.
Start the walkthrough- 1 Request · Procurement
- 2 UAE checks · NexaPair, automatically Preview
- 3 Connections · Compliance
- 4 Score · Risk
- 5 Decision · Compliance
- 6 Central Bank · Risk and Legal
- 7 Incident · Operations
- 8 Board · Board
Value, not cost
What a joined-up programme is worth to you.
Move the sliders to match your organisation. The estimate counts only time saved, before a single prevented fraud or outage.
How we estimate it
We multiply vendors by hours per vendor, add inspection preparation at eight hours a day, halve the total, and multiply by your hourly cost. Prevented fraud, outages and findings are not counted.
Estimated value each year
Illustrative only. Assumes onboarding, review and inspection preparation take half the time they do today. Your results depend on your starting point.
Two-minute tours
See it working.
Integrations
Plugs into the systems you already run.
REST API, signed webhooks and exports today. Native connectors for the large ERP platforms are on the roadmap.
See what flows each wayFree resources
Download it, use it, stay ahead.
- White paper: Article 13 made practical (PDF)
- Readiness checklist (Excel and PDF)
- Regulation hub: which rules apply to you
See NexaPair with your own vendors.
30 minutes, on your scenarios, in English or Arabic.